
Why Your Passed Security Audit Is Hiding Your Biggest Cyber Risks
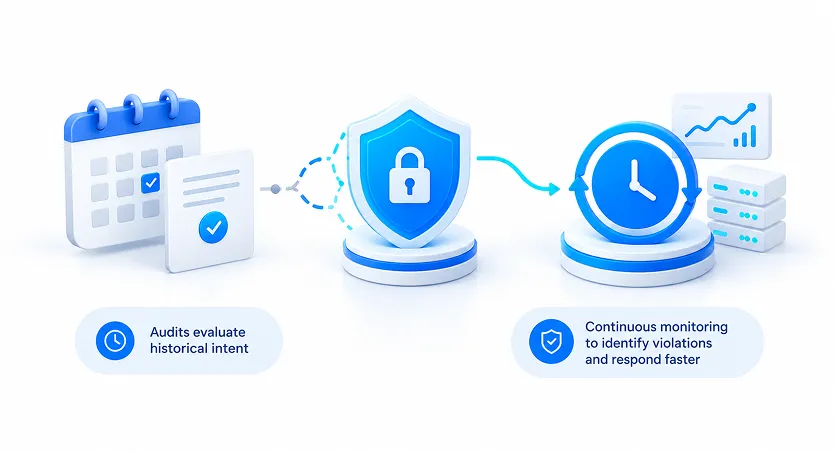
Static compliance audits create a false sense of security; continuous cyber operations demand real-time telemetry and automated controls.
Why is traditional compliance failing enterprise security?
In From Compliance to Continuous Cyber Operations by ServiceNow Workflow, the authors argue that annual check-the-box audits leave massive security blind spots between reporting cycles.
Audits evaluate historical intent, not current security posture. However, the source understates the cultural resistance from risk teams accustomed to manual sampling. As ServiceNow notes, teams must shift to "continuous monitoring to identify violations and respond faster."How do platform admins operationalize continuous posture?
According to the ServiceNow Policy and Compliance Management Documentation, combining Integrated Risk Management (IRM) with SecOps on one platform automates control testing across hybrid assets.
Automated control testing eliminates periodic audit fire-drills (Note: Source is promotional). What's missing is a clear strategy for legacy, non-API systems that cannot feed real-time telemetry into the CMDB. Compliance is merely the static byproduct of continuous operational hygiene; if you secure the live workflow, the audit takes care of itself.