
ServiceNow Vault Console: What It Actually Does for Data Security and Compliance
Protecting sensitive enterprise information across cloud environments is no longer just an IT task it is a core business requirement. As regulatory pressures mount and generative AI capabilities process vast amounts of operational data, maintaining control over sensitive information requires centralized oversight. The ServiceNow Vault Console provides platform administrators, security officers, and compliance leads with a unified command center to manage, monitor, and enforce data protection policies across their entire ServiceNow ecosystem.
At TopTech, we analyze how modern security frameworks integrate into day-to-day enterprise operations. In this guide, we break down what the ServiceNow Vault Console actually delivers, how it safeguards your data, and how your organization can leverage it to simplify regulatory audits.What Is the ServiceNow Vault Console?
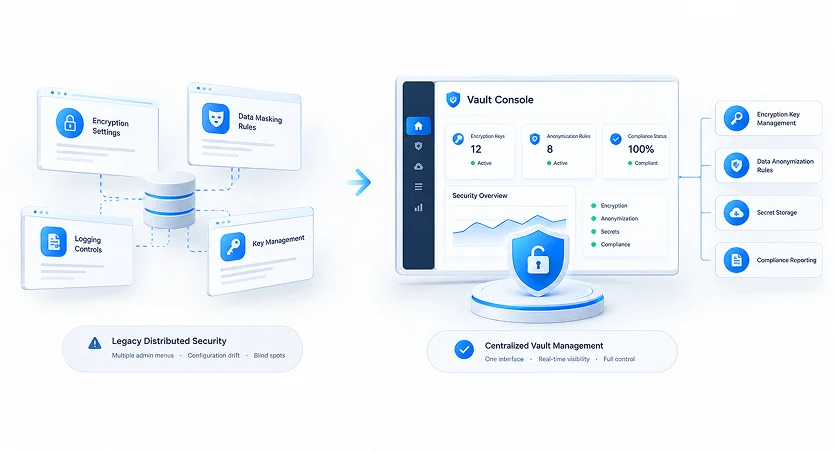
The ServiceNow Vault Console is a centralized administrative workspace designed to manage the suite of security, privacy, and encryption applications that make up ServiceNow Vault. Rather than navigating disconnected settings across separate platform modules, security teams can use this single dashboard to configure data protection rules, monitor active encryption keys, track anonymization schedules, and audit system compliance status in real time.
By unifying these security tools into a single operational interface, the console bridges the gap between high-level compliance policies and technical execution.Traditional Security Controls vs. Centralized Vault Management:
Legacy Distributed Security: Requires setting up encryption, data masking, and logging controls across multiple disconnected admin menus, leading to configuration drift and blind spots.Centralized Vault Console: Consolidates encryption key management, data anonymization rules, secret storage, and compliance reporting into one unified interface with real-time health metrics.Core Security Capabilities & Operational Workflows
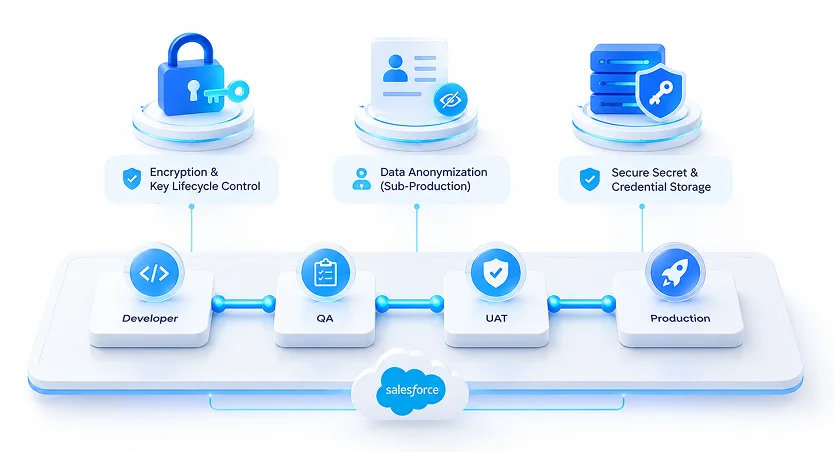
Rather than isolating security tools into separate administrative buckets, the ServiceNow Vault Console coordinates four essential protection mechanisms into a single, continuous workflow.
- Column-Level Encryption & Key Lifecycle Control: Provides granular encryption for specific fields and database tables containing PII or financial details. Through the console, security teams manage the complete key lifecycle including automated rotation, bring-your-own-key (BYOK) configurations, and access policies ensuring data stays protected both at rest and in transit.
- Automated Data Anonymization Across Sub-Production: Enforces rule-based masking and obfuscation of personal details when instances are cloned or refreshed. This allows developers, testers, and third-party vendors to work in realistic non-production environments without exposing authentic customer or employee data.
- Encrypted Secret & Credential Storage: Replaces hardcoded passwords, access tokens, and API keys with secure, central storage. The console monitors integration credentials, automates secret rotation schedules, and prevents exposure across automated orchestration flows.
- Proactive Data Loss Prevention (DLP): Applies real-time scanning policies to inspect incoming form inputs, attachments, and chat logs. If a user accidentally pastes confidential credit card details or proprietary code into a support ticket, the system flags or blocks the input before it is saved to the core database
Strategic Value: Why Centralized Data Protection Matters for AI and Compliance
As organizations expand their use of generative AI and automated workflows, securing underlying platform data becomes critical. The ServiceNow Vault Console provides three strategic advantages for modern enterprise IT teams:
Safe Enterprise AI Deployment
Generative AI tools like Now Assist rely on continuous access to operational records to summarize tickets, generate responses, and automate case routing. The Vault Console allows security leads to enforce strict data anonymization and field-level encryption before records feed into AI models. This ensures AI features operate on clean, compliant context without risking exposure of sensitive personal information.Streamlined Regulatory Audits
Proving compliance to external auditors often requires assembling evidence from dozens of system logs. The console simplifies this process by providing visual health indicators, configuration tracking, and exportable security reports. Administrators can quickly verify that data retention rules are active, encryption keys are properly rotated, and access policies meet regulatory standards like GDPR, HIPAA, and SOC 2.Reduced Administrative Overhead
Managing enterprise security across multiple sub-production and production instances can exhaust IT resources. By centralizing key management, secret storage, and policy configuration into a single dashboard, platform teams reduce setup errors, eliminate duplicate efforts, and maintain consistent security postures across all instances.4 Steps to Maximize Your ServiceNow Vault Deployment
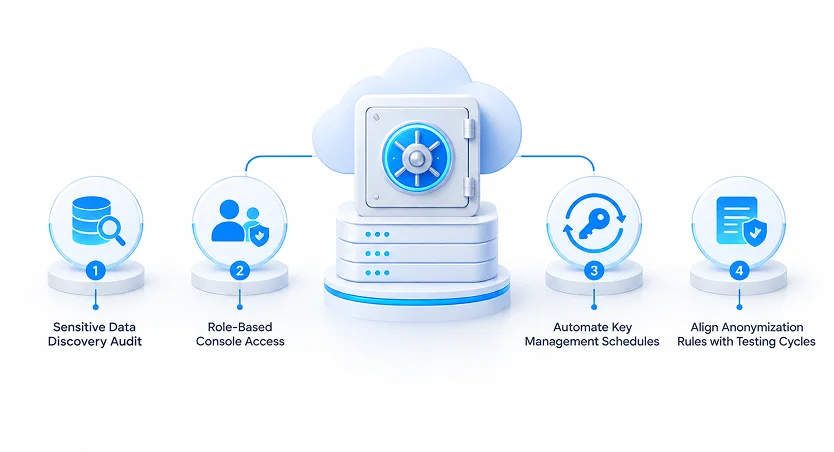
Deploying advanced security tools requires clear governance. At TopTech, we recommend following this four-step strategy to get the most out of your Vault Console implementation:
- Conduct a Sensitive Data Discovery Audit: Identify high-risk fields across your tables such as national ID numbers, credit details, and health records that require column-level encryption or masking.
- Establish Role-Based Console Access: Restrict Vault Console administrative rights exclusively to certified platform security leads to prevent unauthorized policy modifications.
- Automate Key Management Schedules: Configure automated rotation policies for encryption keys and integration secrets within the console to minimize manual key handling.
- Align Anonymization Rules with Testing Cycles: Ensure sub-production environments automatically apply data anonymization scripts during instance cloning to keep development instances secure.
Key Takeaways
- Unified Security Management: The ServiceNow Vault Console serves as a centralized command center to configure, monitor, and audit data protection applications across your instance.
- Integrated Workflow Capabilities: It combines column-level encryption, sub-production data anonymization, secret management, and data loss prevention into an interconnected administrative flow.
- AI-Ready Privacy: By enforcing real-time data masking and encryption, the console ensures generative AI tools like Now Assist run safely on compliant data.
- Audit Efficiency: Centralized logging and visual health metrics streamline compliance reporting for major regulatory frameworks.
Strengthen Your ServiceNow Security Posture with TopTech
Securing complex enterprise platforms against evolving threats requires technical expertise, robust architecture, and clear governance. At TopTech, our platform security certified leads help enterprise teams design, deploy, and optimize ServiceNow Vault configurations to protect sensitive assets while maintaining operational agility.
Ready to enhance your platform security and compliance? Contact our security specialists today to schedule a comprehensive ServiceNow architecture audit.